The Four Key Pillars of an Effective Security Strategy
Before developing a security strategy, it's important to understand the areas it needs to address. An effective approach brings together four interconnected elements.
published on 12/08/2026
Written by Stéphane Couturier
Written by Stéphane Couturier
A security breach is rarely just a technical incident: it can lead to business disruption, data loss, reputational damage and, in some cases, a threat to people's safety. Yet many businesses focus all their attention on cybersecurity while overlooking physical, human and organisational security. Effective protection can never be limited to a single area. It relies on a comprehensive, consistent and continuous business security strategy – a true 360° protection framework. This guide provides a practical methodology for designing, implementing and continuously improving your strategy.
Before developing a security strategy, it's important to understand the areas it needs to address. An effective approach brings together four interconnected elements.
This covers the physical and technological measures used to protect people, premises and assets, including:
Access control systems can include card and fob readers, biometric identification, keypads and smartphone-based credentials. These solutions enable organisations to manage who can access specific areas and at what times, helping prevent unauthorised entry.
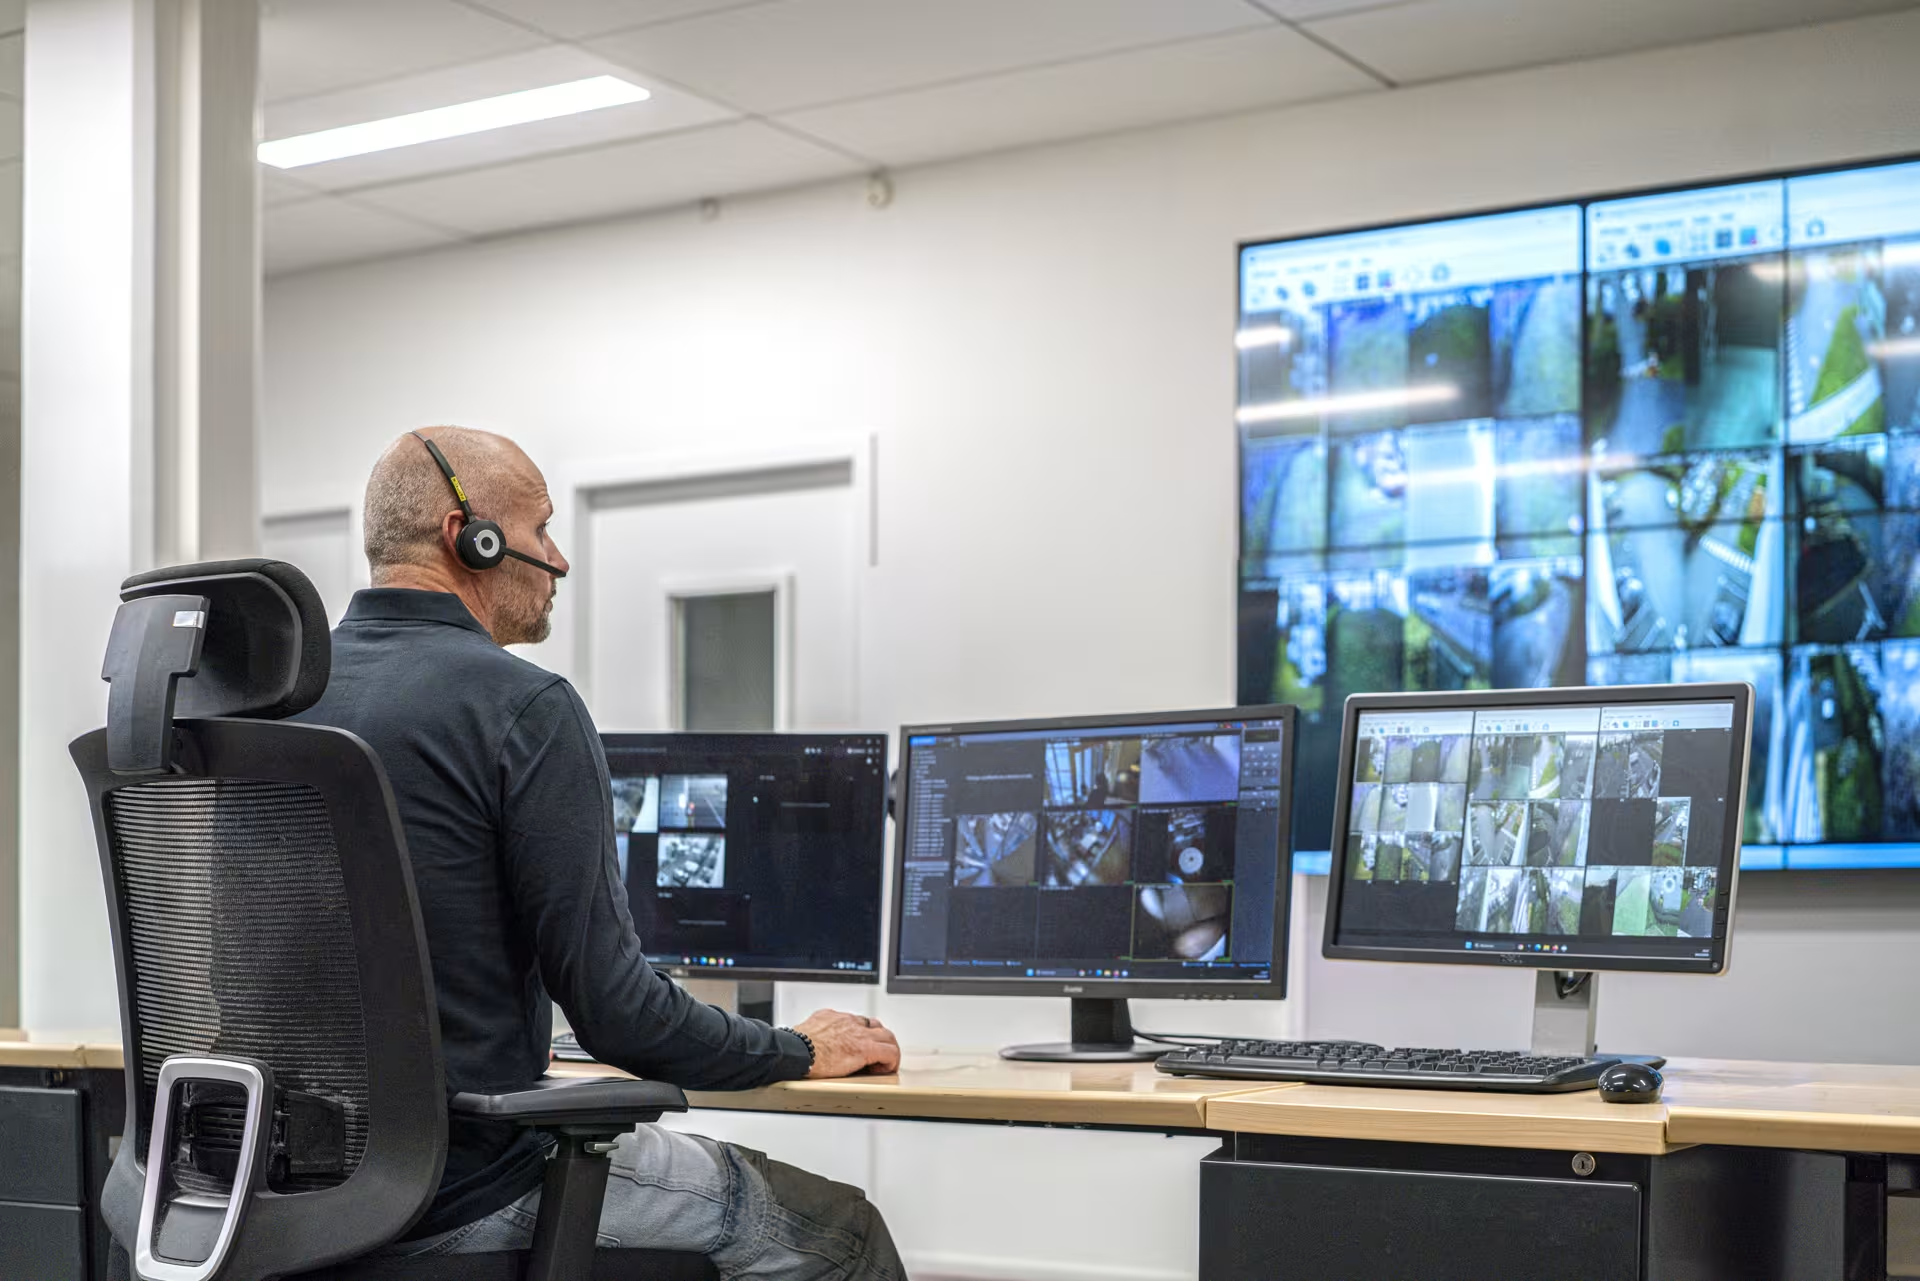
Intruder alarm systems, including motion sensors, vibration detectors and door and window contacts, help identify unauthorised activity. Modern CCTV systems can also incorporate AI-powered video analytics to detect potentially suspicious behaviour and generate alerts, enabling a more proactive approach to security.
Fencing, infrared detection systems, automated gates and security lighting help protect site boundaries and deter unauthorised access. Effective perimeter security provides an important first line of defence, helping identify potential threats before they reach buildings or valuable assets.
The aim is not to become an IT specialist, but to understand the key risks and put appropriate measures in place to manage them.
Customer data, intellectual property, business-critical systems and internal communications. Organisations should identify the information and systems whose loss, theft or compromise could disrupt operations, cause financial losses or damage their reputation.
Ransomware, phishing, data theft and distributed denial-of-service (DDoS) attacks are among the cyber threats businesses need to consider. These attacks can disrupt operations, compromise sensitive information and result in significant financial and reputational damage.
By securing computers and servers with antivirus and endpoint detection and response (EDR) tools, protecting networks with firewalls, controlling access through multi-factor authentication (MFA), and regularly backing up critical data to a separate, secure location.
Effective security depends on people and processes as well as technology. Building a strong security culture helps employees recognise risks, follow procedures and contribute to protecting the organisation.
Key measures include:
This aspect of a security strategy focuses on preparing for deliberate threats and serious security incidents, protecting people and minimising disruption to business operations.
Measures to manage risks associated with aggression and antisocial behaviour, lone worker protection systems and appropriate security arrangements for corporate events.
Establishing clear emergency procedures, including evacuation plans for fires and security threats, responses to unauthorised intrusions, and arrangements for sheltering in place when evacuation is unsafe.
Addressing additional risks such as employee safety during business travel, including destination risk assessments and travel assistance, protecting commercially sensitive information against industrial espionage, and reducing the risk of internal theft.
Follow these seven practical steps to develop a security strategy tailored to your organisation's needs and risks.
A security assessment should help answer three key questions:
Next, assess each risk according to its likelihood and potential impact, including financial, operational and reputational consequences.
Identify the assets that need protecting, including physical assets (buildings, equipment and stock), digital assets (sensitive information and IT systems), and people (employees, contractors and visitors).
Security objectives should follow the SMART framework: Specific, Measurable, Achievable, Relevant and Time-bound.
Practical examples include:
Setting measurable objectives helps organisations monitor progress, assess performance and identify where improvements are needed.
"The strongest strategies we support are those that establish a business objective before choosing the technology. The question is not 'which camera should we install?' but 'what level of business continuity are we aiming for, and what is the cost of an incident we can prevent?' Investment then follows a clear ROI logic."
A security policy provides a consistent framework for managing security across the organisation. It should clearly define:
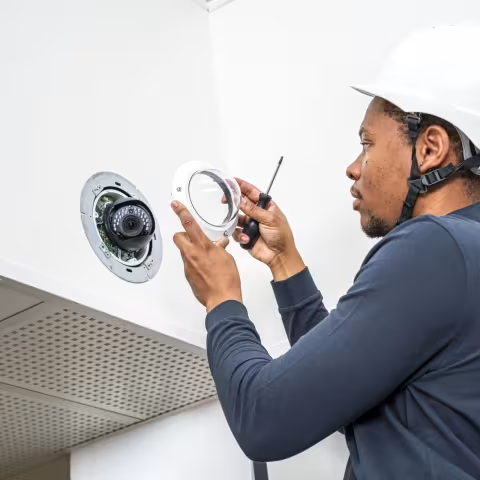
This stage involves putting the right security measures in place, combining technology such as access control, CCTV, intruder alarms, cybersecurity and remote monitoring with clear operational procedures.
Technology is most effective when supported by well-defined processes. For example, an intruder alarm system should be backed by clear procedures for assessing alerts and coordinating an appropriate response.
Investment should be prioritised according to risk, addressing the most significant vulnerabilities first. Where appropriate, organisations can integrate existing systems and introduce improvements in phases to manage costs and minimise disruption.
Employees play an important role in maintaining effective security. Regular training, practical exercises and awareness campaigns help staff recognise potential threats, follow established procedures and respond appropriately to incidents.
Training should address relevant risks, including unauthorised access, phishing and unsafe security practices. Ongoing communication and refresher training help reinforce good habits and embed security awareness throughout the organisation.
No security system can eliminate every risk. Having clear incident response procedures helps organisations act quickly, protect people and minimise disruption when an incident occurs.
Effective procedures should include:
Incident response procedures should be regularly reviewed and tested through practical exercises to ensure employees understand their responsibilities and identify areas for improvement.
Security risks change over time, so an effective strategy should be regularly reviewed and updated.
This includes assessing security performance, reviewing incidents, identifying emerging threats and evaluating whether existing measures remain appropriate.
Independent security assessments can also provide valuable insights, helping organisations identify overlooked vulnerabilities and opportunities for improvement.
An effective business security strategy goes beyond individual systems and technologies. It requires an integrated approach that brings together physical security, cybersecurity, people and processes, and business continuity.
By regularly assessing risks, reviewing security measures and involving employees, organisations can strengthen their protection and respond more effectively to emerging threats.
Security should be viewed as a long-term investment, helping to protect business operations, maintain customer confidence and safeguard valuable assets.
Is your security strategy strong enough to address today's risks? Contact the SCUTUM experts for a comprehensive audit and a roadmap tailored to your organisation.
A clear security strategy helps businesses protect their people, premises, data and critical operations.
It enables organisations to identify vulnerabilities, prioritise security measures and take a coordinated approach to managing risks.
An effective strategy can also help minimise disruption, reduce potential financial losses and maintain customer confidence in the event of a security incident.
Businesses should assess security risks based on their likelihood and potential impact, including consequences for employee safety, operations, finances and reputation.
Priority should be given to threats affecting critical assets, sensitive information and essential business systems, particularly where an incident could endanger people or cause significant disruption.
This risk-based approach helps organisations focus resources on the areas where security improvements are most needed.
A business security strategy should be reviewed regularly, ideally at least once a year, to ensure it remains appropriate as risks and business requirements change.
Additional reviews should be carried out following significant organisational changes, the introduction of new systems or premises, security incidents, or changes to relevant legislation and industry standards.
Regular reviews help businesses identify emerging vulnerabilities and ensure their security measures remain effective.
An experienced security partner can provide specialist expertise and an independent perspective, helping businesses identify vulnerabilities, assess priorities and develop appropriate security measures.
External support can also help organisations make informed decisions, integrate existing systems and avoid unnecessary investment.
Scutum combines expertise in fire and security technologies with integrated solutions and professional monitoring services. Working with an experienced provider can help businesses take a more coordinated approach to protecting their people, premises and operations.
Take action. Request your security maturity audit from the SCUTUM teams and receive a practical roadmap to build, strengthen or update your security strategy.